The Lock on the List
Cisco sells security. So we checked the government's list.
The list
Cisco sells security. The US government's list of flaws that attackers are known to be using carries 101 Cisco entries, and two of CISA's last five emergency directives were about Cisco products.
The list belongs to CISA, the US cyber defence agency. Every flaw on it is one that attackers have used. Not maybe. Used. Its name is the Known Exploited Vulnerabilities Catalog, and on 23 October 2026 its feed carried 1,756 entries. Each has a CVE number, a vendor and product, the date it was added, a due date for federal agencies and a required action.
“Apply mitigations in accordance with vendor instructions … or discontinue use of the product if mitigations are unavailable.”
CISA, Known Exploited Vulnerabilities Catalog, the required action · read 24 October 2026
101 entries
As of 23 October 2026, Cisco had 101 entries on the list. Fifty were added in 2022, while the catalogue filled in its back list. The next three years added 7, 6 and 8.
Source: CISA, Known Exploited Vulnerabilities Catalog (the JSON feed, catalogVersion 2026.10.23); CISA, Emergency Directives 25-03 and 26-03; CISA's directives listing and its news release of 8 January 2026; Cisco Systems, Form 10-K for fiscal 2026 (SEC EDGAR, CIK 0000858877)
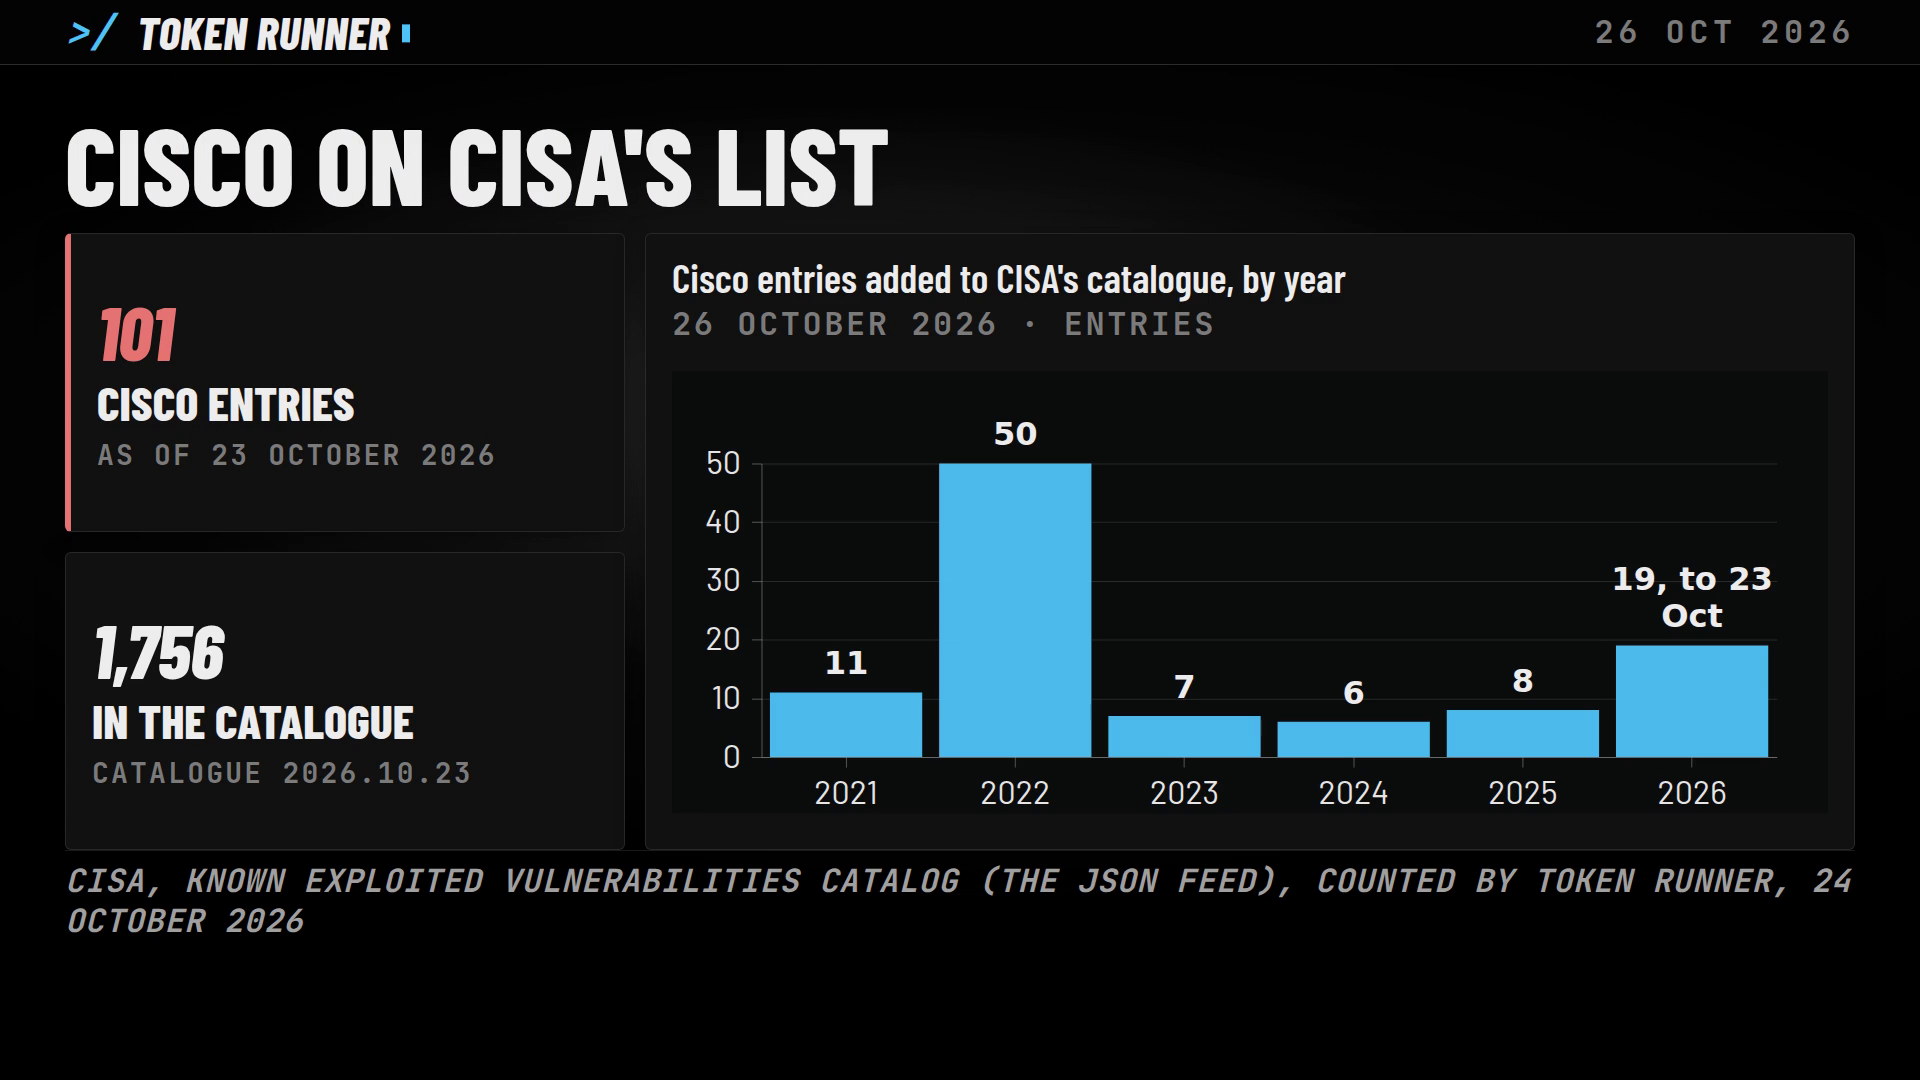
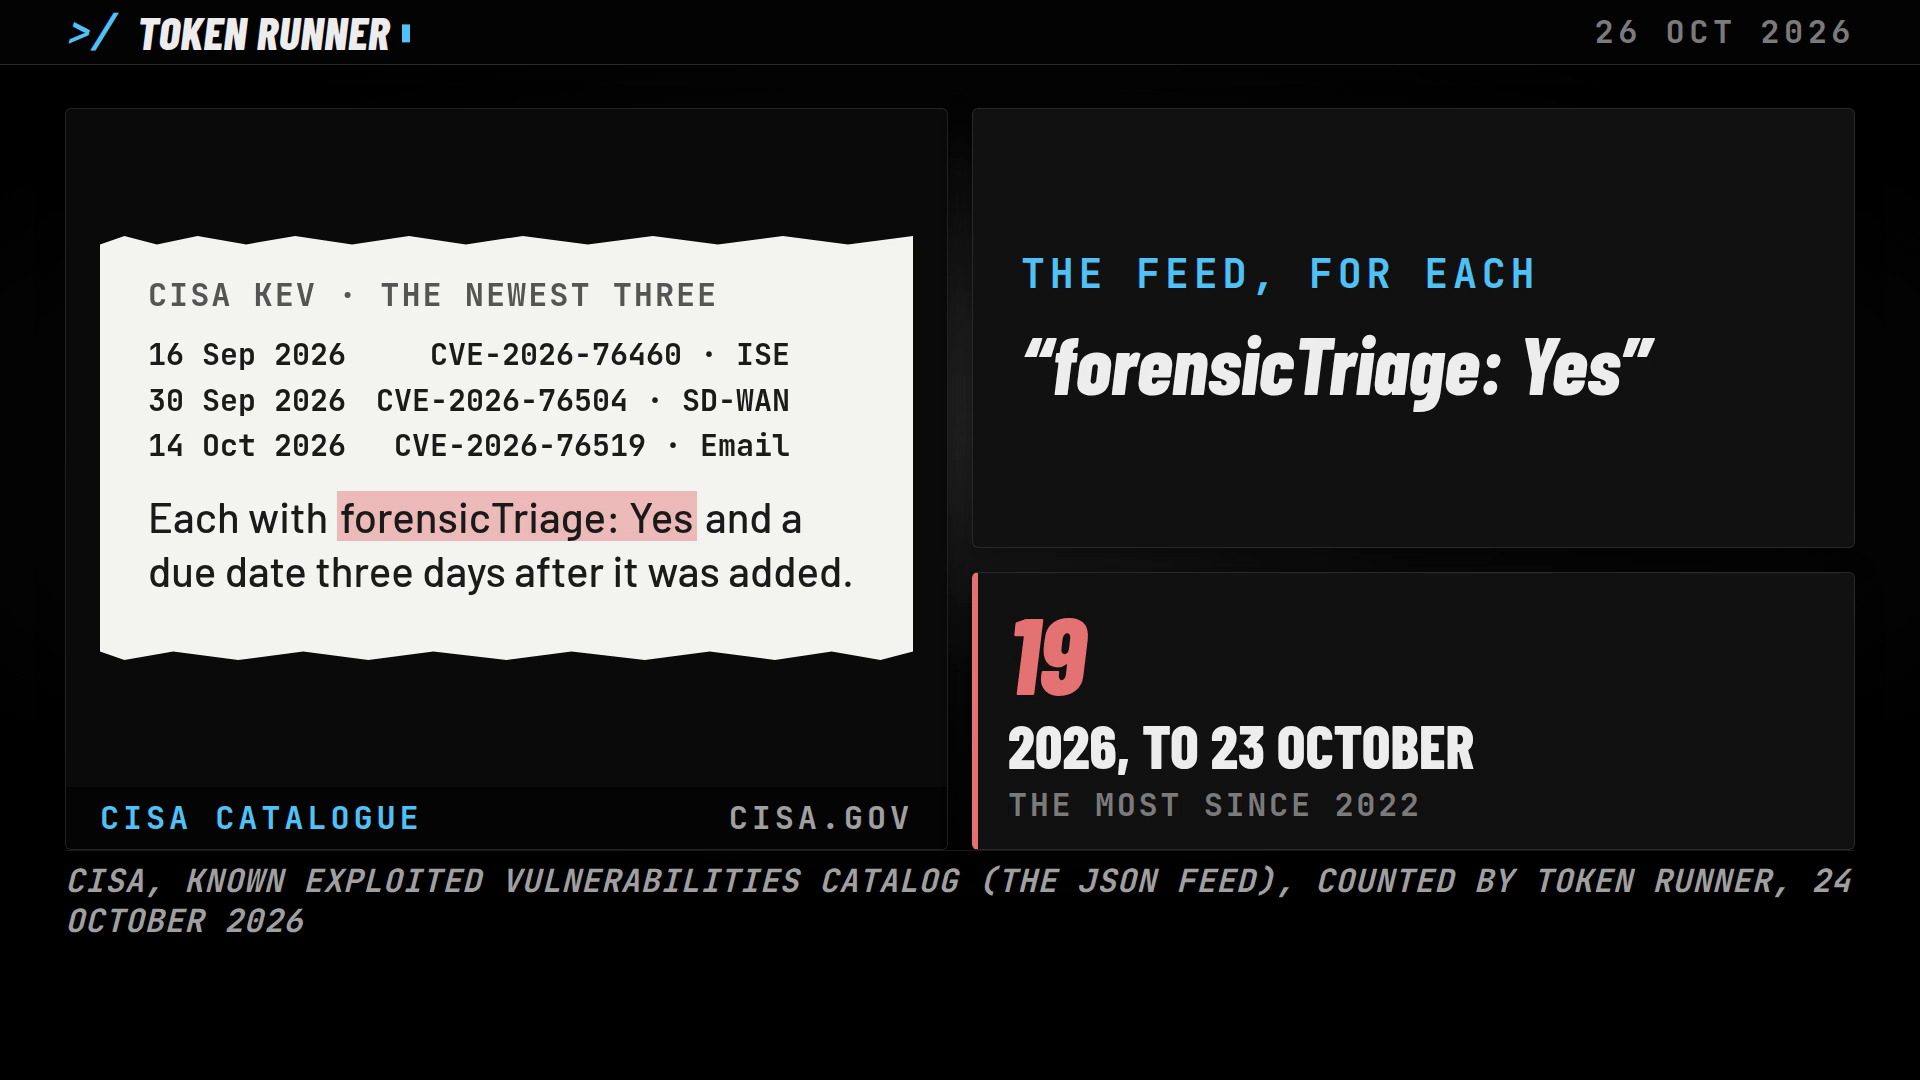
This year the catalogue has added 19 Cisco entries so far. That is more than in any year since 2022, with two months still to go. The newest three: CVE-2026-76460 in Identity Services Engine, added 16 September 2026; CVE-2026-76504 in Catalyst SD-WAN Manager, 30 September; CVE-2026-76519 in Secure Email Gateway, 14 October. Each was due for a fix three days after it was added.
The count is by the year an entry was added, not the year a flaw was found. CISA created the catalogue in November 2021 and back-filled older exploited flaws, which is why 2021 and 2022 carry 61 of the 101. The catalogue's own groupings of Cisco products are uneven ("IOS and IOS XE Software" 14 entries, "Adaptive Security Appliance (ASA) and Firepower Threat Defense (FTD)" 6, "IOS XR" 6, "Catalyst SD-WAN Manager" 5). So this piece counts entries, not products, and ranks Cisco against no other vendor: the catalogue counts nobody's installed base.
The directives
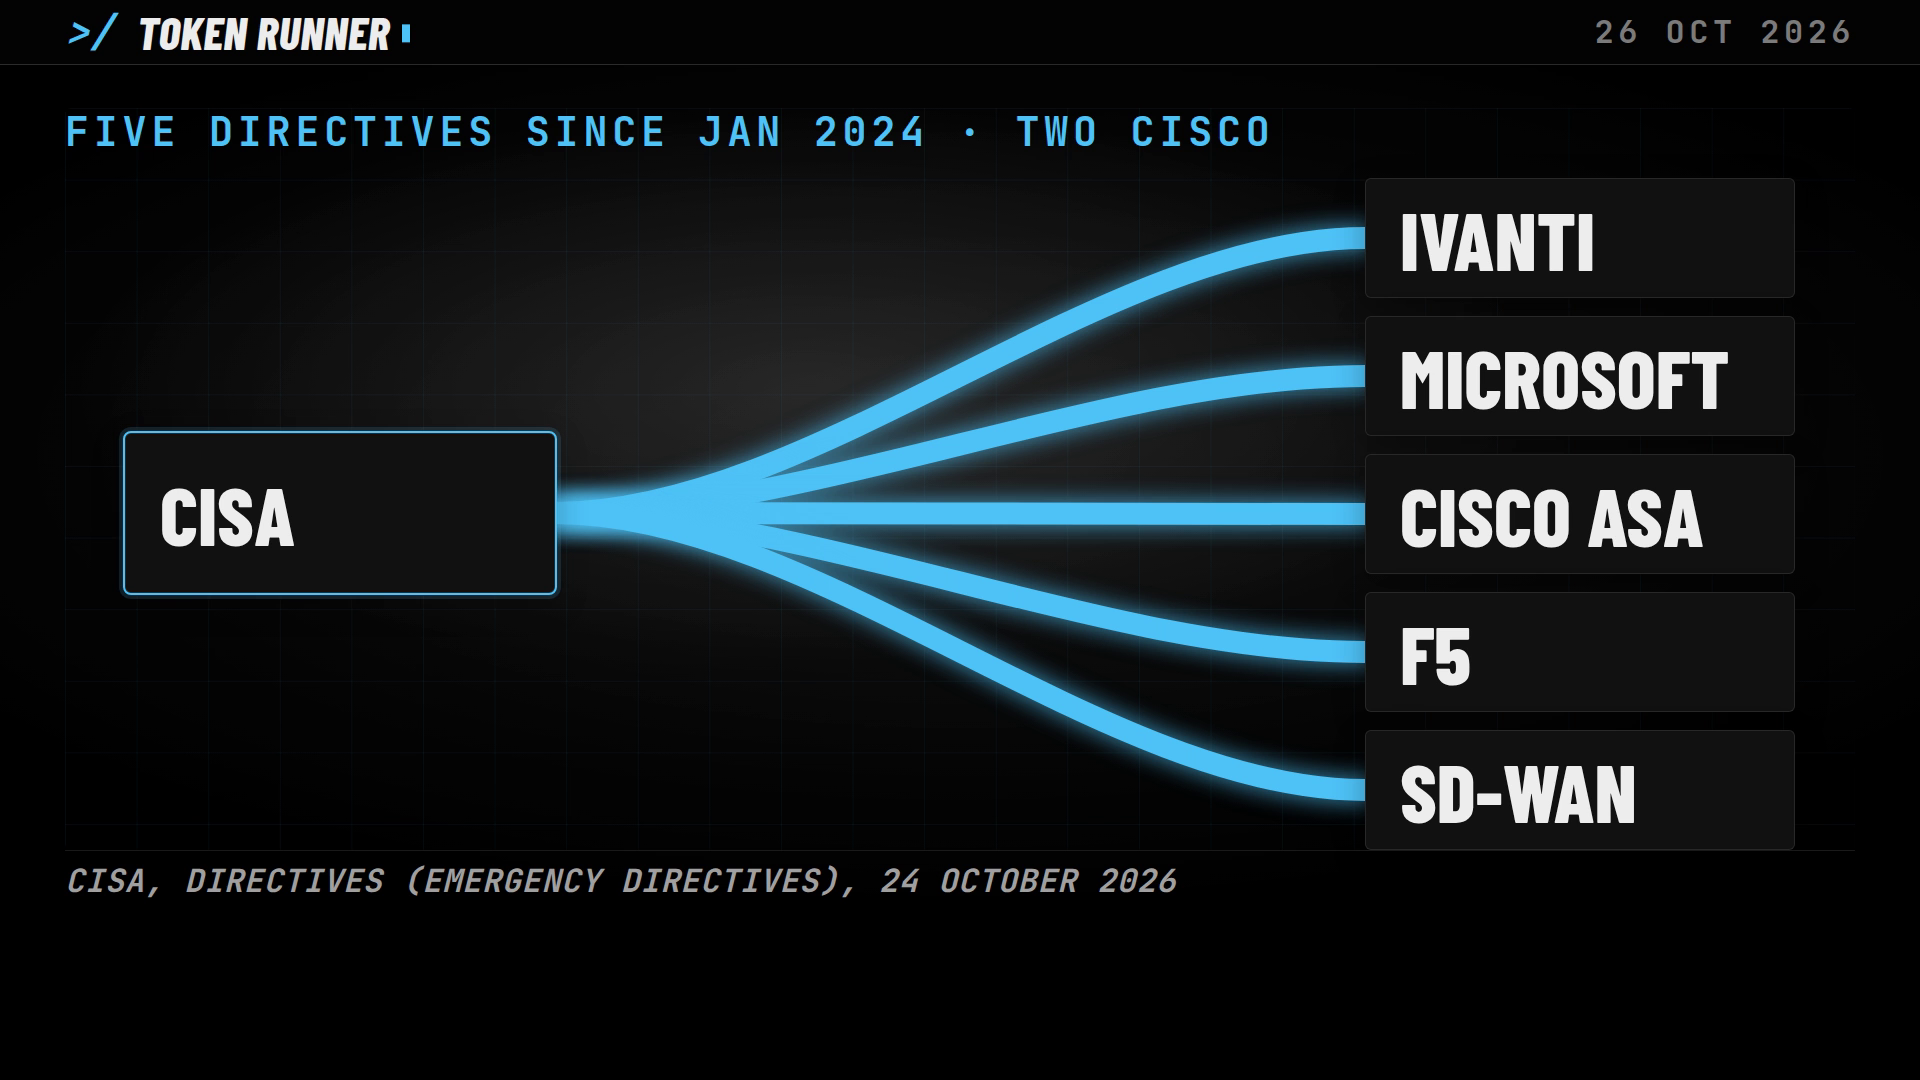
CISA's emergency directives are orders to every federal agency: drop everything. Since January 2024, CISA lists five that are still in force. Ivanti, Microsoft and F5 have one each. Cisco has two: its ASA firewalls and its SD-WAN.
The five on CISA's listing: ED 24-01 on Ivanti Connect Secure and Policy Secure (19 January 2024); ED 25-02 on Microsoft Exchange (7 August 2025); ED 25-03 on Cisco ASA firewalls (25 September 2025); ED 26-01 on F5 devices (15 October 2025); ED 26-03 on Cisco SD-WAN (25 February 2026). On 8 January 2026 CISA retired ten older directives of 2019 to 2024 at once. So the listing shows the directives in force, not every directive ever issued. A directive does not reach contractors.
The first order
The first came on 25 September 2025: hunt for compromise on Cisco's ASA firewalls. CISA named an advanced threat actor that manipulated read-only memory to survive a reboot and a system upgrade.
The directive opens: "CISA is aware of an ongoing exploitation campaign by an advanced threat actor targeting Cisco Adaptive Security Appliances". It adds: "Cisco assesses that this campaign is connected to the ArcaneDoor activity identified in early 2024".
The clock
Agencies had one day to hand over memory dumps and one week for a full inventory. Five months later the second directive, on Cisco's SD-WAN, gave them two days to patch.
Source: CISA, Known Exploited Vulnerabilities Catalog (the JSON feed, catalogVersion 2026.10.23); CISA, Emergency Directives 25-03 and 26-03; CISA's directives listing and its news release of 8 January 2026; Cisco Systems, Form 10-K for fiscal 2026 (SEC EDGAR, CIK 0000858877)
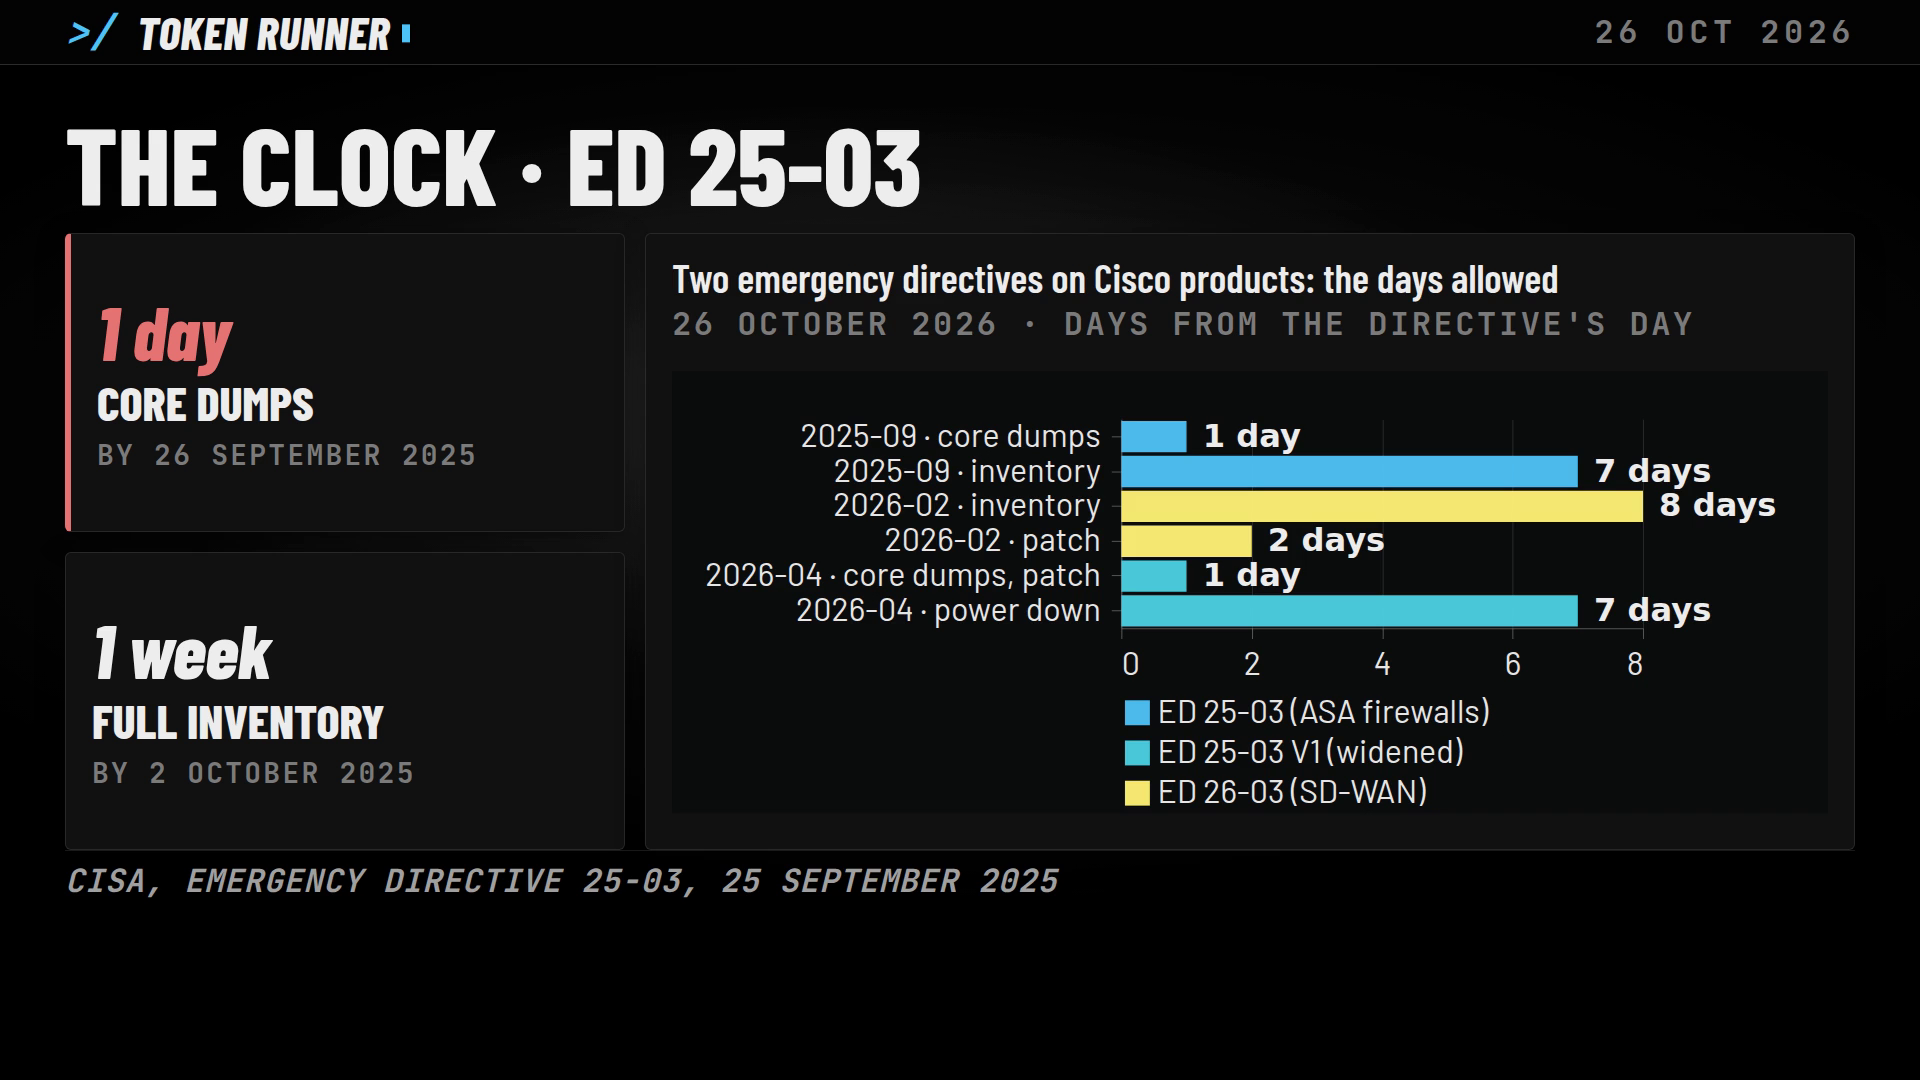
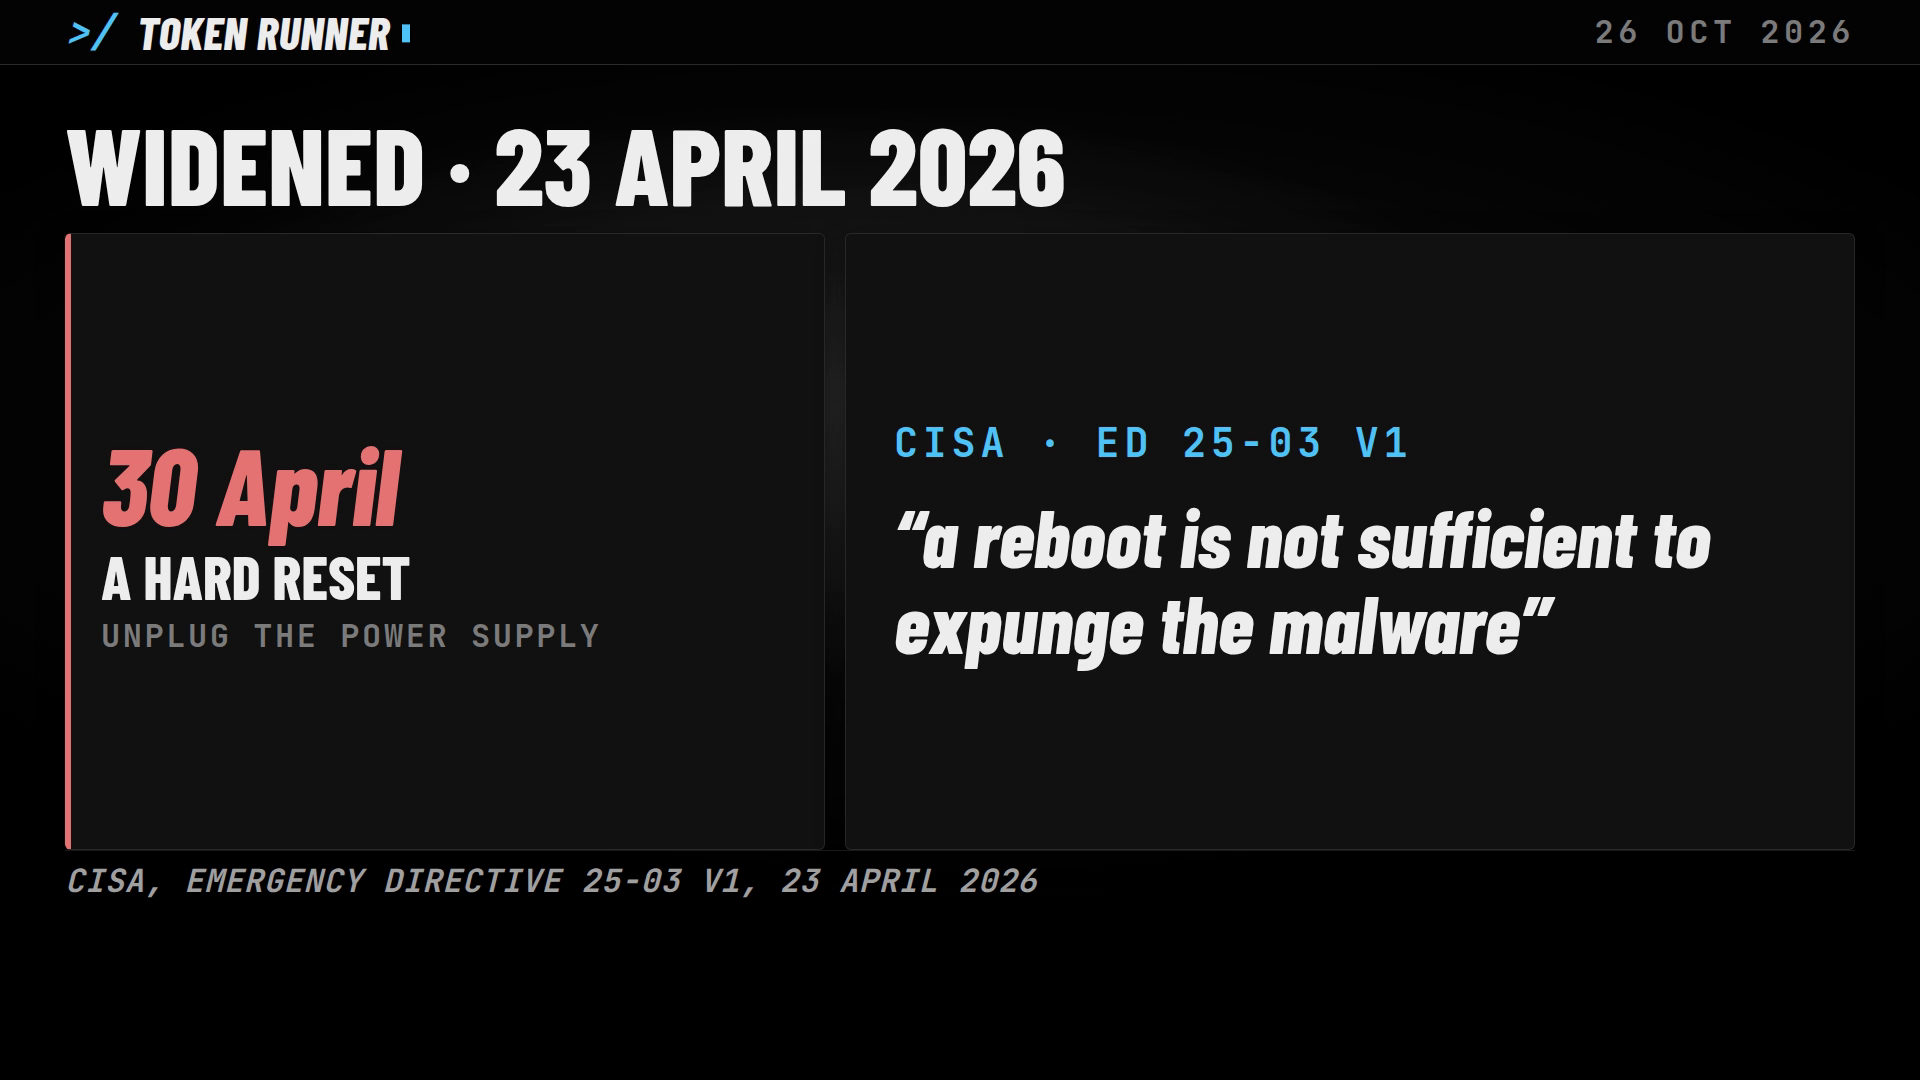
In April 2026 CISA widened the firewall order. This time a reboot was not enough. Agencies had to unplug the power supply by 30 April.
The dates, from the directives themselves. ED 25-03: core dumps to CISA "by 11:59PM EST on September 26, 2025"; a complete inventory "By 11:59 PM EST on October 2, 2025". ED 26-03: identify every in-scope SD-WAN system and report by 26 February; Cisco's updates applied by 5:00 PM ET on 27 February; a detailed inventory by 5 March, a hardening report by 12 March, logs to CISA by 23 March; and if a root account is compromised, "Rebuild control management plane". ED 25-03's V1 of 23 April 2026 widened the first order to the Firepower and Secure Firewall series: core dumps and patches by 24 April, the hard reset by 30 April, an inventory by 1 May.
ArcaneDoor
Cisco's own researchers had named the campaign a year and a half earlier: ArcaneDoor. In Cisco's words, a state-sponsored actor, going after the perimeter of government networks around the world.
Cisco Talos, 24 April 2024: the actor is "now tracked as UAT4356 by Talos", and "we assess with high confidence that these actions were performed by a state-sponsored actor." Talos named the two backdoors "Line Runner" and "Line Dancer", and dated the actor's infrastructure "back to early November 2023". The further victims "all of which involved government networks globally." Talos names no country, and neither does this piece.
The security business
Cisco's security products brought in $8.2 billion in fiscal 2026, up 2%. That is one category of five, out of $63.3 billion in all.
Source: CISA, Known Exploited Vulnerabilities Catalog (the JSON feed, catalogVersion 2026.10.23); CISA, Emergency Directives 25-03 and 26-03; CISA's directives listing and its news release of 8 January 2026; Cisco Systems, Form 10-K for fiscal 2026 (SEC EDGAR, CIK 0000858877)
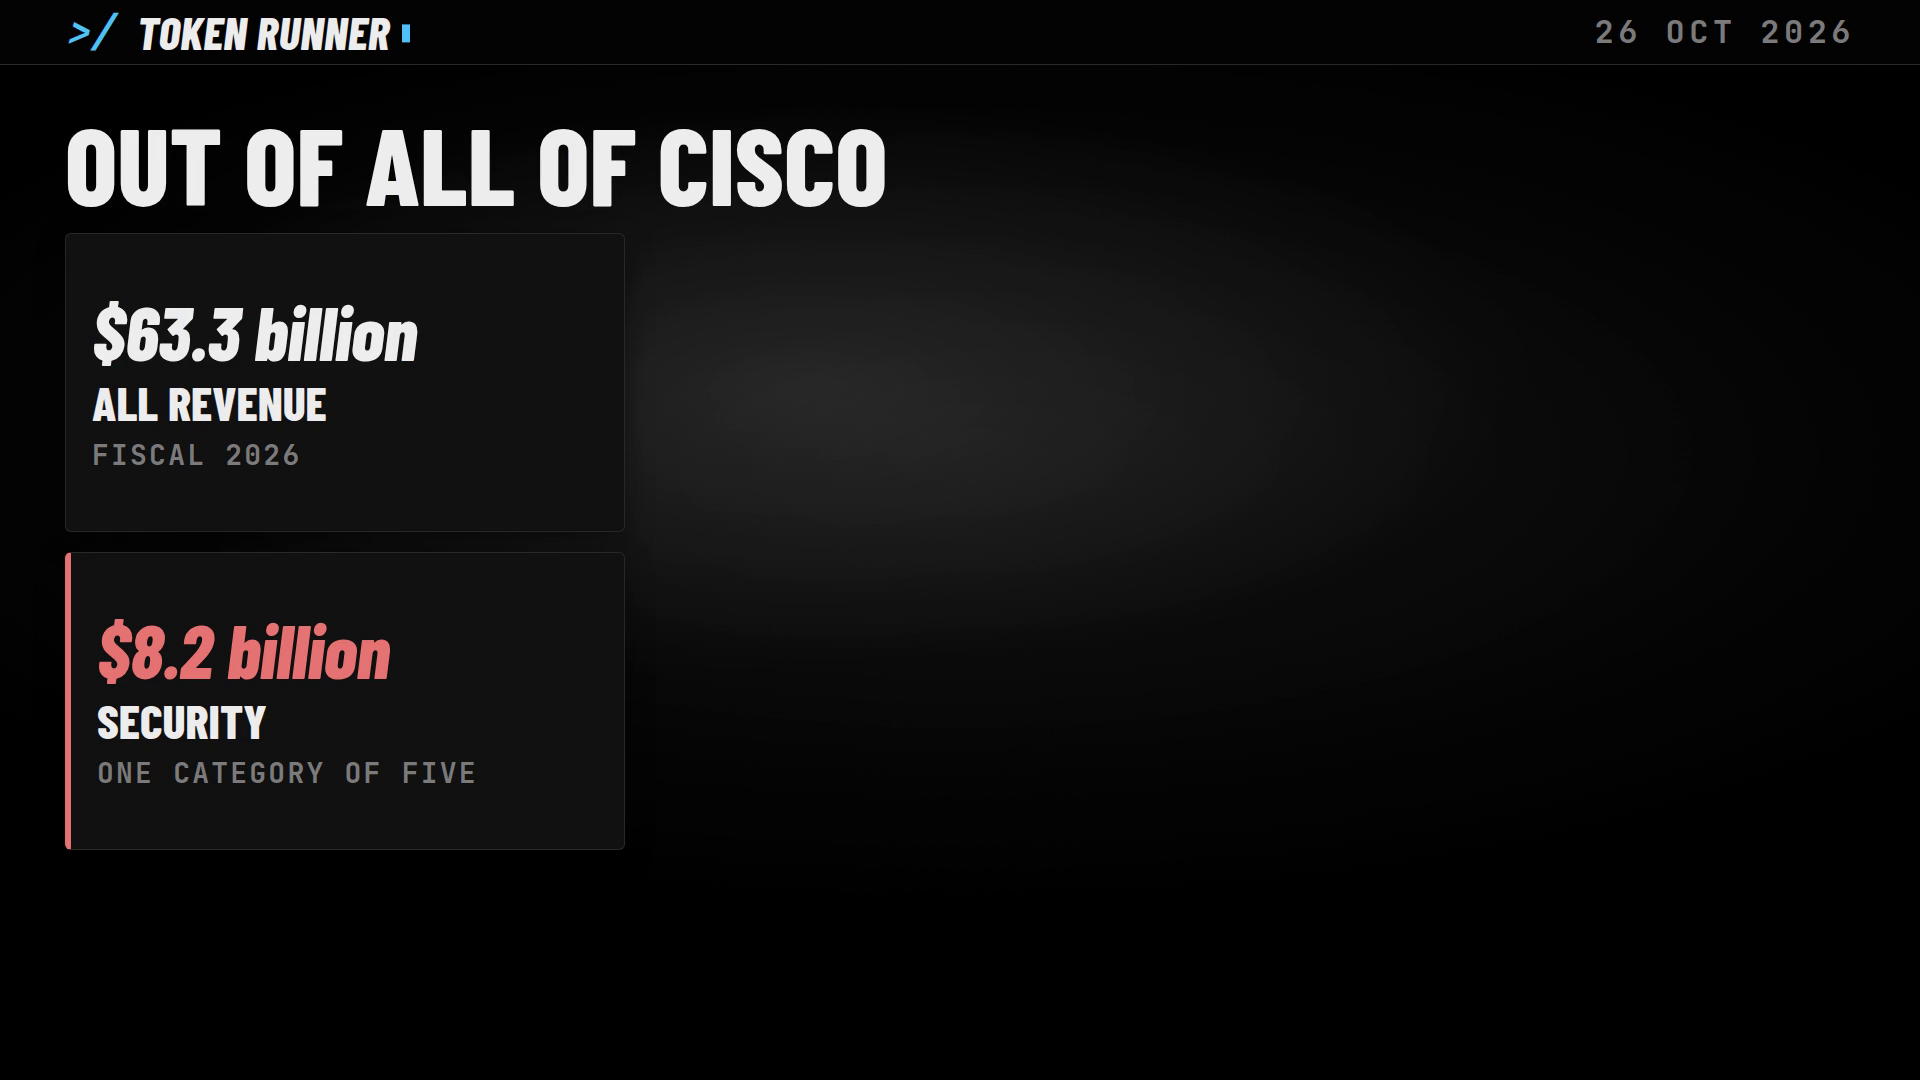
Cisco's 10-K for fiscal 2026 gives revenue by product category: Networking $34,668 million, Services $15,030 million, Security $8,232 million (about $8.2 billion), Collaboration $4,300 million and Observability $1,095 million; $63,325 million in all, about $63.3 billion.
To be fair
Cisco gear runs a huge share of the world's networks. More boxes make more targets. The list counts flaws used against Cisco, not how Cisco compares with anyone else. And Cisco patched these.
Cisco published fixes for CVE-2025-20333 and CVE-2025-20362 on 25 September 2025, the day of the directive, with no workarounds. The persistence issue of April 2026 got its own advisory on 23 April 2026, the day CISA widened the order: "the ArcaneDoor threat actor has developed a previously unknown persistence mechanism" in the Firepower operating system.
On the list
A company that sells security sits on the government's list of flaws in active use 101 times, 19 of them this year.
Source: CISA, Known Exploited Vulnerabilities Catalog (the JSON feed, catalogVersion 2026.10.23); CISA, Emergency Directives 25-03 and 26-03; CISA's directives listing and its news release of 8 January 2026; Cisco Systems, Form 10-K for fiscal 2026 (SEC EDGAR, CIK 0000858877)
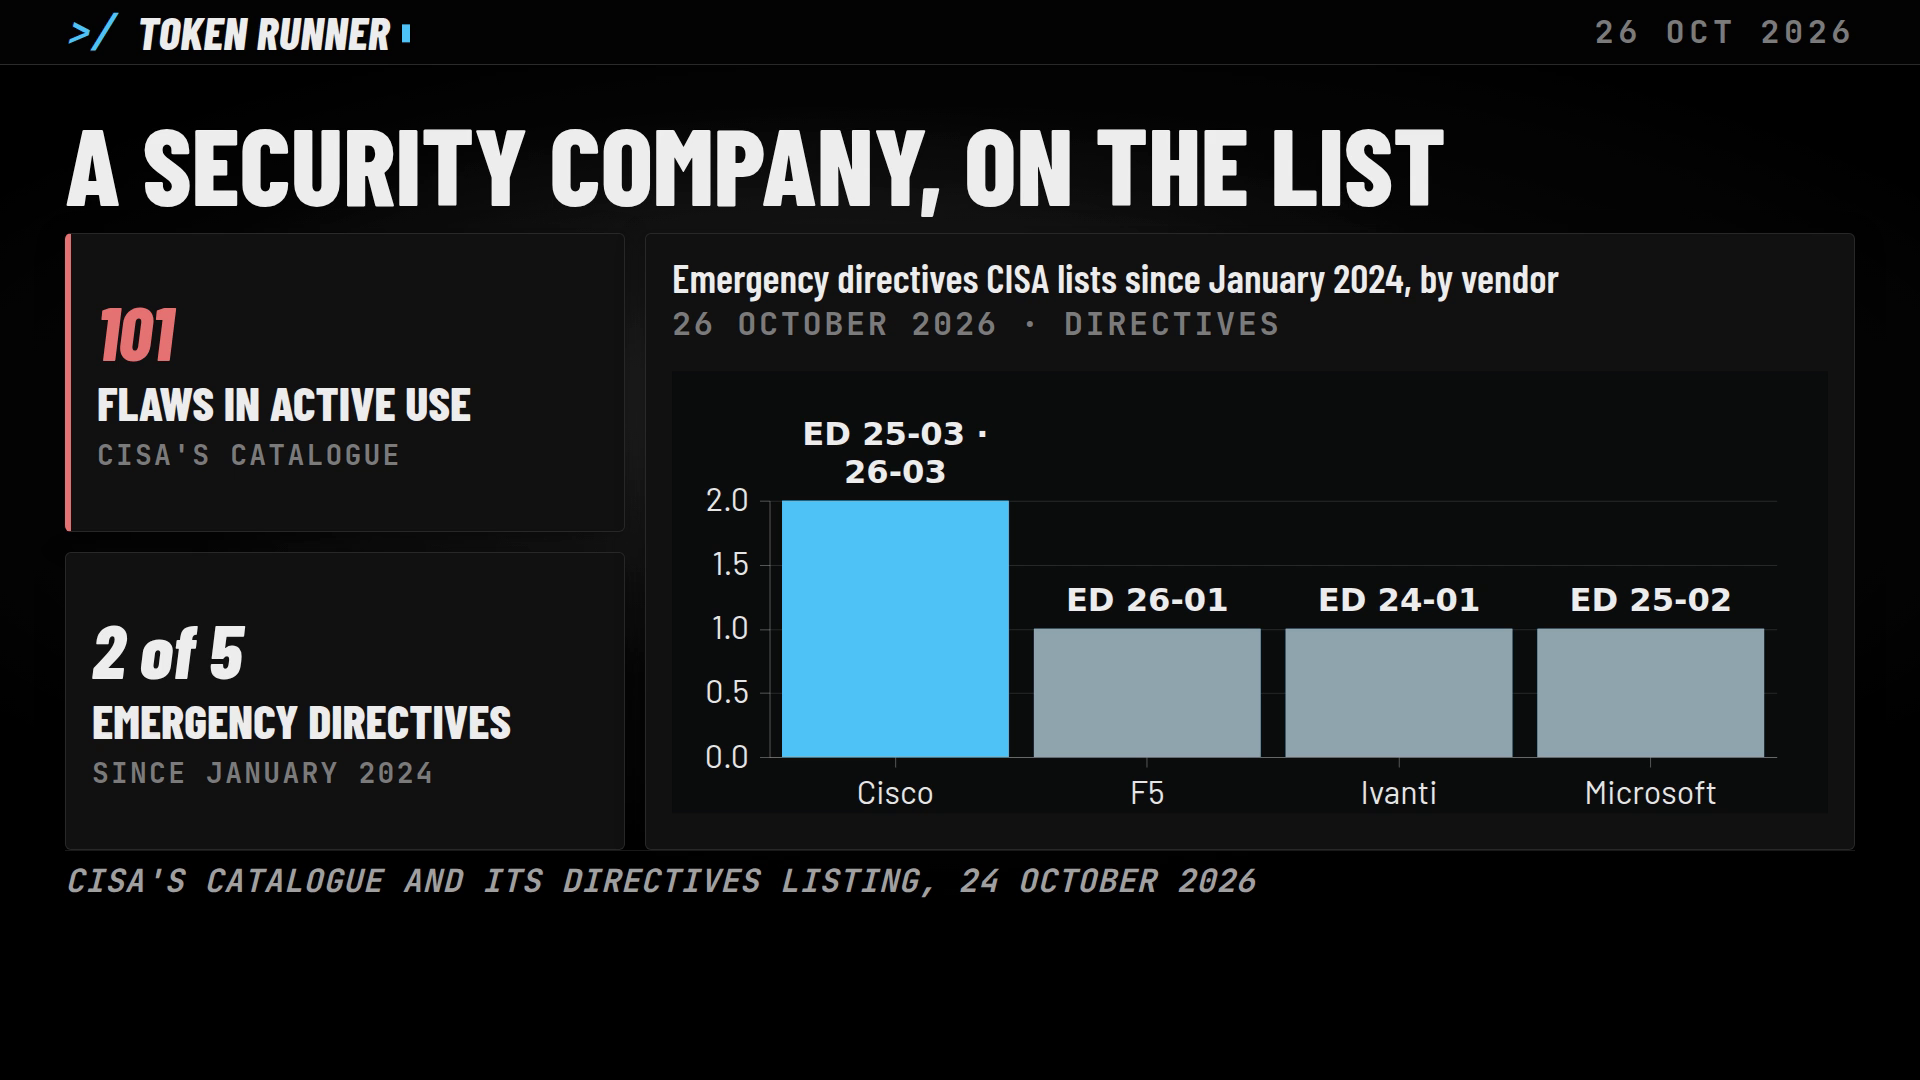
Two of the five emergency directives CISA has in force were about its products, and the second one followed the first by five months.
The catalogue's feed is public and updated as entries are added. A twentieth Cisco entry for 2026 would show there first.
Every figure from CISA's catalogue, its directives, and Cisco's own filing.
Sources
- CISA, Known Exploited Vulnerabilities Catalog, the JSON feed: catalogVersion 2026.10.23, released 23 October 2026, 1,756 entries; 101 with the vendor Cisco, by the year added 11 (2021), 50 (2022), 7 (2023), 6 (2024), 8 (2025), 19 (2026, to 23 October). Counted by Token Runner from the feed on 24 October 2026. The catalogue was created in November 2021 under BOD 22-01 and back-filled older exploited flaws, so the 2021 and 2022 counts include that back-fill.
- CISA, Emergency Directive 25-03, "Identify and Mitigate Potential Compromise of Cisco Devices", 25 September 2025, and its V1 of 23 April 2026: "CISA is aware of an ongoing exploitation campaign by an advanced threat actor targeting Cisco Adaptive Security Appliances"; "manipulating read-only memory (ROM) to persist through reboot and system upgrade."; core dumps "by 11:59PM EST on September 26, 2025"; a complete inventory "By 11:59 PM EST on October 2, 2025"; "Cisco assesses that this campaign is connected to the ArcaneDoor activity identified in early 2024"; V1: core dumps and patches by 24 April 2026, "a reboot is not sufficient to expunge the malware", a hard power reset by 30 April, an inventory by 1 May 2026.
- CISA, Emergency Directive 26-03, "Mitigate Vulnerabilities in Cisco SD-WAN Systems", 25 February 2026 (V1 of 11 March 2026): "CISA is aware of a cyber threat actor's ongoing exploitation of Cisco SD-WAN systems."; CVE-2026-20127 and CVE-2022-20775; identify every in-scope system by 11:59 PM ET on 26 February 2026; Cisco's updates applied by 5:00 PM ET on 27 February 2026; a detailed inventory by 5 March, a hardening report by 12 March, logs to CISA by 23 March 2026; on a root compromise, "Rebuild control management plane"; "This Directive applies to all federal information systems managed on agency networks"; "This Directive does not apply to contractors".
- CISA, Directives, the listing filtered to Emergency Directives, read 24 October 2026: ED 24-01 Ivanti (19 January 2024), ED 25-02 Microsoft Exchange (7 August 2025), ED 25-03 Cisco (25 September 2025), ED 26-01 F5 (15 October 2025), ED 26-03 Cisco SD-WAN (25 February 2026); and CISA's news release of 8 January 2026, "CISA Retires Ten Emergency Directives, Marking an Era in Federal Cybersecurity": ten directives of 2019 to 2024 retired at once.
- Cisco Talos, "ArcaneDoor: New espionage-focused campaign found targeting perimeter network devices", 24 April 2024: "ArcaneDoor is a campaign that is the latest example of state-sponsored actors targeting perimeter network devices"; "we identified a previously unknown actor now tracked as UAT4356 by Talos."; "we assess with high confidence that these actions were performed by a state-sponsored actor."; the two backdoors "Line Runner" and "Line Dancer"; "we identified actor-controlled infrastructure dating back to early November 2023"; "The investigation that followed identified additional victims, all of which involved government networks globally."; CVE-2024-20353 and CVE-2024-20359.
- Cisco Security Advisories: cisco-sa-asaftd-webvpn-z5xP8EUB (CVE-2025-20333, Critical, CVSS 9.9) and cisco-sa-asaftd-webvpn-YROOTUW (CVE-2025-20362), first published 25 September 2025 at 16:00 GMT, fixed releases only, no workarounds; cisco-sa-asaftd-persist-CISAED25-03, "Continued Evolution of Persistence Mechanism Against Cisco Secure Firewall Adaptive Security Appliance and Secure Firewall Threat Defense", first published 23 April 2026: "the ArcaneDoor threat actor has developed a previously unknown persistence mechanism" residing in "the Cisco Firepower eXtensible Operating System (FXOS)".
- Cisco Systems, Form 10-K for the fiscal year ended 25 July 2026, filed 2 September 2026, Management's Discussion and Analysis: revenue by product category, Networking $34,668 million, Security $8,232 million, Collaboration $4,300 million, Observability $1,095 million, Services $15,030 million, total $63,325 million; "Revenue in our Security product category increased by 2%, or $0.1 billion, primarily driven by growth in our SASE and Network Security offerings."; "Total revenue was $63.3 billion, an increase of 12% compared with fiscal 2025."